
Overview
This guide describes how to configure the AgileSec Platform to run behind a reverse proxy. These configuration changes are applied post-install in completed AgileSec On-Prem deployments.
Clients reach the platform through the reverse proxy's external address and port. The proxy then forwards the request to the Frontend Node's external address and port.
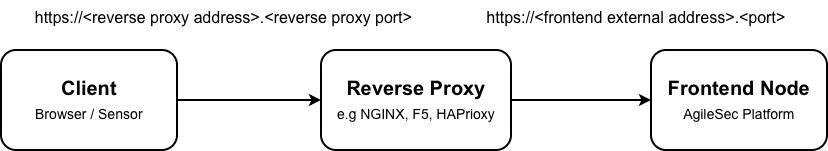
To set up reverse proxy, edit the files listed below and substitute your reverse proxy's address and port for every <reverse proxy address>:<reverse proxy port> placeholder shown.
Set Environment Variables
Set the installation directory variable $agilesec_installation_dir to easily copy and paste guide instructions into terminal:
$agilesec_installation_dir=</path-to-agilesec-installation>
1. API Config
File: $agilesec_installation_dir/config_envs/api
Nodes: Frontend
INGESTION_SERVICE="https://<reverse proxy address>:<reverse proxy port>"

ACS_URL="https://<reverse proxy address>:<reverse proxy port>/osdashboards/_opendistro/_security/saml/acs/idpinitiated"
ACS_DOMAIN_SSO="https://<reverse proxy address>:<reverse proxy port>"

CORS_WHITE_LIST="https://<reverse proxy address>:<reverse proxy port>"

FRONTEND_BASE_URL="https://<reverse proxy address>:<reverse proxy port>"

LINK_CDN="https://<reverse proxy address>:<reverse proxy port>"
2. Web UI Config
File: $agilesec_installation_dir/config_envs/webui
Nodes: Frontend
NEXT_PUBLIC_API_SERVER_URL="https://<reverse proxy address>:<reverse proxy port>"

NEXTAUTH_URL="https://<reverse proxy address>:<reverse proxy port>"
NEXTAUTH_URL_INTERNAL="https://<reverse proxy address>:<reverse proxy port>"

NEXT_PUBLIC_SENSOR_INGEST_URL="https://<reverse proxy address>:<reverse proxy port>"
3. CBOM Config
File: $agilesec_installation_dir/config_envs/cbom
Nodes: Frontend
FILE_HOST_NAME="https://<reverse proxy address>:<reverse proxy port>/fe1"
4. OpenSearch IDP Metadata
File: $agilesec_installation_dir/services/opensearch/config/opensearch-security/idp-metadata.xml
Nodes: Frontend and Backend
Set the reverse proxy address and port in the SingleSignOnService and SingleLogoutService elements
<EntityDescriptor xmlns="urn:oasis:names:tc:SAML:2.0:metadata" entityID="ui_idp">
    <IDPSSODescriptor protocolSupportEnumeration="urn:oasis:names:tc:SAML:2.0:protocol">
        <KeyDescriptor use="signing">
            <ds:KeyInfo xmlns:ds="http://www.w3.org/2000/09/xmldsig#">
            <ds:X509Data>
                <ds:X509Certificate>--idp-cert-pem--</ds:X509Certificate>
            </ds:X509Data>
            </ds:KeyInfo>
        </KeyDescriptor>
        <SingleSignOnService Binding="urn:oasis:names:tc:SAML:2.0:bindings:HTTP-Redirect" Location="https://<reverse proxy address>:<reverse proxy port>/sso"/>
        <SingleLogoutService Binding="urn:oasis:names:tc:SAML:2.0:bindings:HTTP-Redirect" Location="https://<reverse proxy address>:<reverse proxy port>/signout"/>
    </IDPSSODescriptor>
</EntityDescriptor>
5. OpenSearch Security Config
File: $agilesec_installation_dir/services/opensearch/config/opensearch-security/config.yml
Nodes: Frontend and Backend
Update kibana_url under saml_auth section with the reverse proxy address and port.
saml_auth: # any name is fine for this part
  order: 4 # the order of auth to use, relevant when we have multiple auth types
  description: "SAML provider" # A description, any description is fine
  http_enabled: true
  transport_enabled: false
  http_authenticator:
    type: saml
    challenge: true
    config:
      idp:
        metadata_file: opensearch-security/idp-metadata.xml
        entity_id: ui_idp
      sp:
        entity_id: os_sp #example value from our demo setup: demo-saml
      kibana_url: https://<reverse proxy address>:<reverse proxy port>/osdashboards/app/dashboards # i.e https://demo.agilesec-isg.dev/analytics
      roles_key: opensearch_role #This key is used to associate external saml users with internal roles to give them permissions with opensearch security, more details below
      exchange_key: "<exchange key>" #The key to sign the token. The algorithm is HMAC-SHA512, so it should have at least 64 characters, and base64 URL encoding. This key doesn't need to be put anywhere else. It can be generated with `openssl rand -base64 64`
  authentication_backend:
    type: noop
After updating config.yml, run the following on backend-1 only:
JAVA_HOME=$agilesec_installation_dir/bin/java

cd $agilesec_installation_dir/services/opensearch/plugins/opensearch-security/tools

./securityadmin.sh \
  -f $agilesec_installation_dir/services/opensearch/config/opensearch-security/config.yml \
  -t config \
  -icl -nhnv \
  -cacert $agilesec_installation_dir/certificates/ca/agilesec-rootca-cert.pem \
  -cert $agilesec_installation_dir/certificates/<agilesec_internal_domain>/opensearch-admin-user-cert.pem \
  -key $agilesec_installation_dir/certificates/<agilesec_internal_domain>/opensearch-admin-user-key.pem
6. MongoDB IDP Metadata Config
Nodes: backend-1
Run the following commands on backend-1 to update idp-metadata config stored in MongoDB:
METADATA_ESCAPED=$(sed -e 's/\\/\\\\/g' -e 's/"/\\"/g' $agilesec_installation_dir/services/opensearch/config/opensearch-security/idp-metadata.xml | awk '{printf "%s\\n", $0}')

$agilesec_installation_dir/bin/mongosh "mongodb://backend-1.<agilesec_internal_domain>:27017/platform" \
  --tls \
  --tlsCAFile $agilesec_installation_dir/certificates/ca/agilesec-rootca-cert.pem \
  --tlsCertificateKeyFile $agilesec_installation_dir/certificates/<agilesec_internal_domain/[admin-user-combo-cert-key.pem | mongodb-admin-user-combo-cert-key.pem] \
  --authenticationMechanism MONGODB-X509 \
  --authenticationDatabase '$external' \
  --eval 'db.settings.updateOne({ name: "idp-metadata" }, { $set: { value: "'"${METADATA_ESCAPED}"'" } })'
View idp-metadata in MongoDB to confirm its been updated:
$agilesec_installation_dir/bin/mongosh "mongodb://backend-1.<agilesec_internal_domain>:27017/platform" \
  --tls \
  --tlsCAFile $agilesec_installation_dir/certificates/ca/agilesec-rootca-cert.pem \
  --tlsCertificateKeyFile $agilesec_installation_dir/certificates/<agilesec_internal_domain/[admin-user-combo-cert-key.pem | mongodb-admin-user-combo-cert-key.pem] \
  --authenticationMechanism MONGODB-X509 \
  --authenticationDatabase '$external' \
  --eval 'printjson(db.settings.findOne({ name: "idp-metadata" }))'